Anthropic lends its "bug-hunting" AI to hospitals: good news?
Sixteen years. That's how old a bug was that had been sleeping in FFmpeg, the free video engine found in VLC and a whole bunch of apps that play your videos. Test robots had run booby-trapped videos through this piece of code five million times without seeing a thing. It was an AI from Anthropic, Claude Mythos, that found it this spring. And since October 6, that AI is no longer reserved for Apple, Google and Microsoft: Anthropic is opening it up to small hospitals, municipal water utilities and volunteers who maintain free software. And frankly, it's one of the best pieces of news I've read this week!
The hospital technician has just been given a colleague. It doesn't take a coffee break
A sixteen-year-old bug, and another twenty-seven-year-old one
Let's go back a bit. In April, Anthropic introduces Mythos, a model so good at finding vulnerabilities that it refuses to sell it. A vulnerability is an error in software that lets someone get in where they shouldn't. Instead of selling Mythos, Anthropic lends it to around forty large organizations, in a club called Project Glasswing, so they can plug the holes before hackers find them.
And Mythos really came out with the heavy stuff right away. The FFmpeg bug, slipped into the code in 2003 according to an analysis picked up by the specialist press. And a twenty-seven-year-old bug in OpenBSD, a system reputed to be one of the safest in the world, often installed on firewalls, those boxes that filter everything entering a company's network. All it took was opening a connection to the machine to crash it remotely. Twenty-seven years that experts had been rereading this code! When I read that, I thought to myself: “but what were they doing, all that time?” Well, they were looking, like humans do, and a human gets tired, skips a line, goes to get a coffee.
Happy birthday, little bug. That was the last one
129,000 vulnerabilities in four months
The figure Anthropic publishes with the announcement makes your head spin: between April and July, the club's members found at least 129,000 verified vulnerabilities. More than 33,000 are classified as serious or critical, meaning a hacker could use one to take control of a machine or steal data. Anthropic found another 5,500 on its side, combing through free software, whose code is public and that everyone uses without knowing it.
These are corporate figures, it has to be said. They come from the reports of only 33 partners, and Anthropic says the real total is at least five times higher. I can believe it, but I have no way to verify it. What is certain is that tens of thousands of holes are being plugged in software running on your systems. That's concrete!
Who gets what
The Glasswing club disappears, folded into a broader three-tier program, and the first tier, the most open one, which Anthropic calls Defense Access, targets the security teams of companies, associations, universities and government agencies, but above all, and this is written in black and white in the announcement, “critical infrastructure operators of any size, such as regional hospitals or municipal utilities,” small security outfits, volunteers who maintain free software, and researchers who have already reported vulnerabilities. You read that right: volunteers! These are precisely the people who have never had the means to pay for a team of ten experts.
The second tier is reserved for companies that are paid to attack a network with its owner's permission, just to see whether it holds up. The third, the freest one, is reserved for a handful of organizations that test systems whose failure would cause enormous damage: airplanes, power grids, transfers between banks. Those are screened with the American government.
Why everyone doesn't get access to it
Because the tool that finds the flaw in order to patch it also knows how to find it in order to get in. Anthropic published a test that shows it very well: fifty simulated attack missions. With a normal account, Claude refuses everything, from the very first question. With “defense” access, it still refuses 46 out of 50. With “authorized attack” access, it no longer refuses any of them, and Claude Opus 5.5 succeeds in 34 missions out of 50. Exactly as many as without any protection.
The master key is behind the counter. And you show your card
It's the same logic as Google with Gemini 4 Argon, also reserved for defenders last week. And on the same day as Anthropic, Mistral did exactly the opposite: its new model, Mistral Large 4, posts record security scores on a test where Claude and GPT score almost zero because they refuse, and it will be downloadable by anyone at the end of October. Two philosophies on the same Tuesday. For me, in this case, Anthropic is right: a tool like that is lent out upon presentation of the card.
What this changes for you
The utility company that manages your town's water, the hospital where you take your children to the emergency room, the little free software that your internet router uses without telling you: these are exactly hackers' favorite targets, because they are important and poorly defended. From now on, they can have their systems checked by an AI that found a twenty-seven-year-old bug where experts had seen nothing. That doesn't make anything invulnerable. But it shifts the advantage toward those who defend, and you don't see that often!
And you have one role, just one, and it's simple: install the updates. All these patched flaws reach you in the form of a notification that you put off until tomorrow. Hackers, for their part, now exploit a flaw in less than 24 hours, Microsoft measured it. An update that waits three weeks is a door that someone repaired and that you leave open.
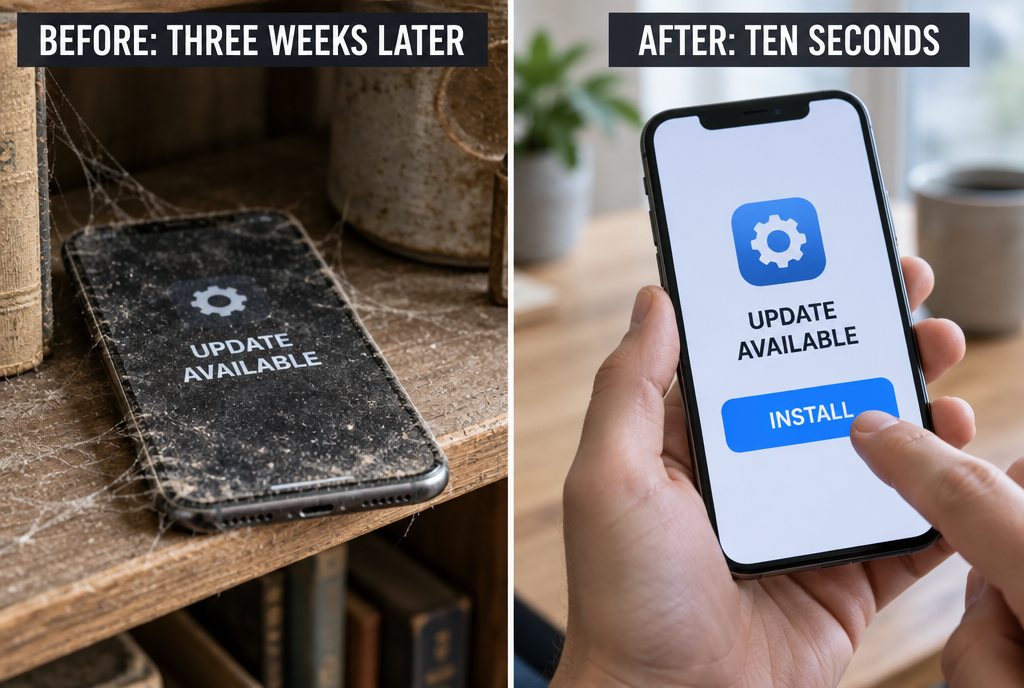
On the left, three weeks of “I'll do it tonight”. On the right, ten seconds
My opinion
I'm rather in favor, and without having to force myself. For years, computer security was a rich person's sport: the bank had its experts, the regional hospital had an overworked IT guy and a printer that jammed. Now, the overworked IT guy gets the same tool as the bank.
Two reservations, though. To enter the program, you have to accept that Anthropic keeps the conversations, to check that nobody misuses the tool. For a hospital having its own systems analyzed, that's not a minor detail. And it's Anthropic, a private company, that decides who is one of the good guys. For now its choices seem good to me, but a bouncer is still a bouncer.
And to the IT guy at the hospital in my region, if you're reading this: sign up, it's on the program page. Hackers, for their part, didn't wait for us to open the door!
Sources
- Anthropic, October 6, 2026: expansion of the Cyber Verification Program
- SiliconANGLE, October 6, 2026: Glasswing folded into a three-tier program
- Anthropic, April 2026: Mythos's security capabilities (OpenBSD and FFmpeg bugs)
- Mistral AI, October 6, 2026: Mistral Large 4 and its security scores
Article written with the help of Claude Code, reread and corrected by me.
Join the conversation
You need an account to comment on this article. Creating one is free and takes under a minute.
No comments yet.