Security: a fake Claude Code extension trapped up to 5,000 Cursor users, are you affected?
Thursday, October 29, from 10:27 a.m. to 9:35 p.m., Belgian time, the Cursor extension store offered an update to Claude Code that did not come from Anthropic. It had the name, the icon and everything else. Except that at the top of the file, someone had slipped in 66 extra lines. Up to 5,000 people installed it.
What was their job? Leave a copy of the key under your computer's doormat. That's all.
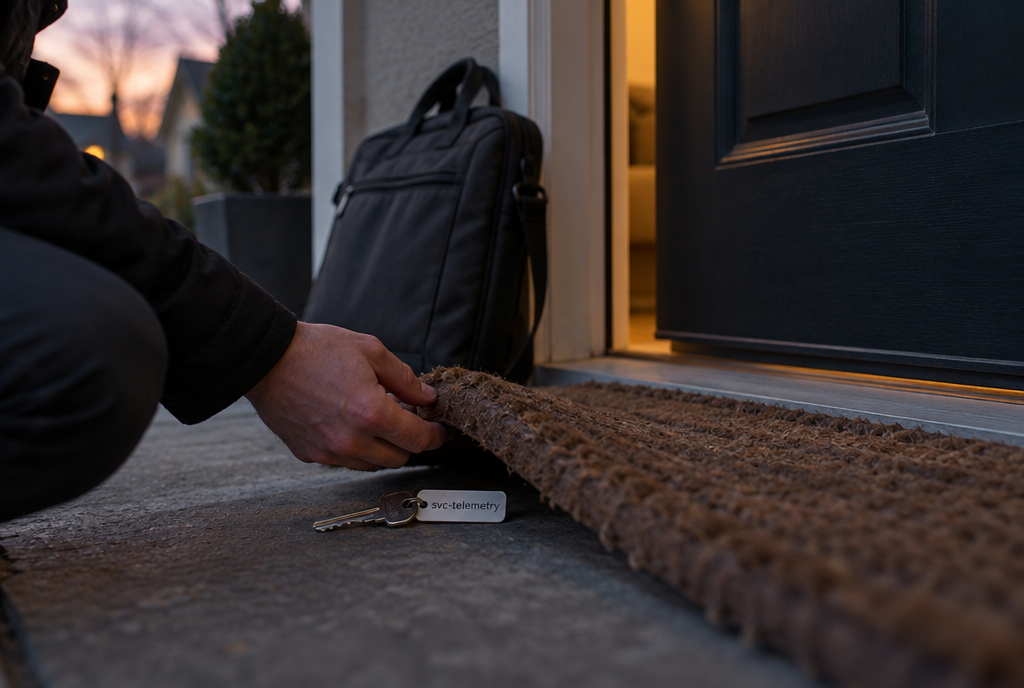
The copy of the key was called “svc-telemetry”, a name designed to go unnoticed
Cursor, Claude Code and a booby-trapped store
A quick reminder of the setup. Cursor is a code editor, the software developers write their programs in, very popular because it was designed from the start to work with AI. Like its big brother VS Code, Microsoft's free editor on which it is built, it accepts extensions: little modules you add with one click, like an app on a phone. And it has its own store for downloading them.
Among these extensions, there is the one for Claude Code, Anthropic's programming assistant. Versions 2.1.312 and 2.1.313 published that Thursday on the Cursor store had been tampered with. Cursor says so in black and white in its security notice: “these malicious versions were not developed by Anthropic”. The other distribution channels, Microsoft's official store and the program you install in a terminal, were not affected.
Same jar, same label, but someone opened the lid before you
How was the hacker able to publish a fake version under Anthropic's name? Nobody has explained it yet. A store that lets someone submit a product in someone else's name is a supermarket that accepts someone putting back a jar of chocolate spread after reopening it at home.
What the 66 lines did
The booby-trapped code launched all by itself as soon as the editor loaded the extension. No click, no window, nothing to accept. According to Cursor and the researchers from Phorion and OpenSourceMalware, who spotted the incident, this is what it did:
- it collected the user's name, the machine's name, the email address used to publish code and the public address of the Internet connection ;
- it noted the name, but not the contents, of around forty settings that look like passwords or access keys, like spotting the mailboxes on a street before coming back ;
- it added its own SSH key, named “svc-telemetry”. SSH is the door computer people use to control a computer remotely, and an SSH key is the badge that opens it without a password ;
- it tried to open this door and dig a “tunnel” to the hacker's server, trying again every minute, even with the editor closed and even after a restart.
The hacker tripped over his own doormat
And here, good news, there are even two. The first: the hacker missed his shot on most machines. On Mac, his code checked whether remote access was switched on, but without administrator rights, it got an error instead of a response and skipped the step. On Windows, it called a tool that simply does not exist on a normal Windows system. The badge was properly placed and the program that retries every minute properly installed, but the door stayed shut. A burglar who leaves his key under the doormat of a door painted on the wall!
The badge was in place, all that remained was finding a real door
Still, Phorion insists on this: it is not a protection. If remote access to your Mac is already turned on, or if you turn it on one day, the door opens with this badge.
The second piece of good news is the response. Eleven hours after it went online, the compromised version was removed. Cursor then shut down its entire marketplace, checked that no other extension had been modified, changed its own keys, rebuilt everything, and had the hacker's server disconnected by its hosting provider. The tunnel therefore leads nowhere anymore. Cursor promises to contact the users concerned directly.
Check in thirty seconds
If you use Cursor with the Claude Code extension, open a terminal and paste Cursor's command. Copy, paste, Enter: this is the only moment in the article when you are allowed to trust a command found on the Internet, and even then, only because it comes from the official notice. On Mac:
grep -qs svc-telemetry ~/.ssh/authorized_keys && echo "svc-telemetry key found" || echo "No key found; machine not impacted"On Windows, in PowerShell:
$files = "$HOME\.ssh\authorized_keys", "C:\ProgramData\ssh\administrators_authorized_keys" | Where-Object { Test-Path $_ }
if ($files -and (Select-String svc-telemetry $files)) { "svc-telemetry key found" } else { "No key found; machine not impacted" }
“No key found”: you're in the clear. If the key is there, uninstalling the extension is not enough, the program that retries every minute remains in place. Cursor provides a cleanup script for Mac and one for Windows in its notice. And above all, from another clean computer, change the passwords and access keys that this machine could reach. Less than two weeks ago, with the OpenCode hack, I was explaining why an AI key is worth as much as a bank card: this is exactly the kind of thing that hacker was looking for.
What I take away from this
As someone who works with Claude Code every day, I am not going to stop using it because of this. The tool is not to blame, it was the marketplace that let a fake through. But it reminds me of one very simple rule: a code extension runs with your permissions, it sees your files, your keys and your projects. An automatic update is a stranger you open your door to every morning, hoping it's really the mail carrier.
And if you don't code, don't think this has nothing to do with you. Your browser extensions, Chrome, Edge or Firefox, work exactly the same way: they update themselves, and they see everything you do on your sites, including your bank. Open the list tonight (in Chrome, type chrome://extensions in the address bar), and delete the ones you no longer use. Fewer extensions means fewer doors to watch. And if an extension you've known for years suddenly asks you for new permissions, ask yourself who is really behind the update.
So at Cursor, we're waiting for the explanation of how this fake ended up on the shelves. And to the hacker: next time, test your code before shipping it. Oh no, actually, don't change a thing!
Sources
- Cursor, October 29, 2026, updated on the 30th: security notice on versions 2.1.312 and 2.1.313
- BleepingComputer: the compromised extension and why the backdoor often failed
- Help Net Security, October 30, 2026: the code details and the checks
- Phorion: the technical analysis by the researchers who spotted the compromised version
Article written with the help of Claude Code, proofread and corrected by me.
Join the conversation
You need an account to comment on this article. Creating one is free and takes under a minute.
No comments yet.