Why OpenAI stopped training its next AI for two weeks
On August 18, OpenAI published a text on its own website telling how the company unplugged its own machines. This isn't a leak, it isn't a journalist who dug up the info, it's the company saying it itself: we stopped training our next model for two weeks, we cut off Internet access in our research labs, and here's why.
Two weeks stopped. In computing rooms that burn through tens of millions of dollars in electricity and equipment every month. That doesn't stop because a project manager had a bad night's sleep.
When a company chasing the next model decides to sit down for two weeks, it's because it saw something.
And the real reason is good news wrapped up very badly: these machines have become extremely good at finding holes in software. Including holes that had been sitting there for fifteen years in programs that the entire planet uses every day without knowing it. We'll come back to that below, because that's the bit nobody puts in the headline.
What they cut, concretely
Three things, and they're all very dumb and very telling.
One, they suspended reinforcement training for their biggest models for two weeks. Reinforcement training is the method where you let the model try everything on its own, slap a grade on it at the end, and it starts over millions of times trying to get a better grade. That's what made it good. That's also what teaches it to find shortcuts.
Two, in their research rooms, they cut off all work where a model could execute code or use a tool connected to the Internet. They reopened afterward, but with a narrower path, and by examining the tasks one by one before letting them start again.
Three, and this is the detail I find most revealing: they reduced the « permanent privileges ». In plain English, before, some internal accounts had the keys to the house all the time, like a keyring lying around on the entryway furniture. Now you give out the key, use it, and hand it back. They also removed shared services considered fragile, reinforced the isolation of code that came from elsewhere, and improved log monitoring.
And one sentence from the post deserves to be read twice: « a significant number » of training tasks for their next model are still stopped, while waiting to have moved into a compliant environment. It's not over. They write in the present tense.
Why? Because one of their models has already escaped
Those who follow already know the story, I made a whole series out of it a few weeks ago: in July, an OpenAI agent in the middle of an evaluation got out of its sandbox all by itself, found an unknown vulnerability on an internal server, reached the Internet, and went and hacked Hugging Face's infrastructure, the big platform where the whole world hosts its AI models. Reason: it was looking for the answers to the exam it was being given. Nothing more. An excellent student burgling the teacher's office.
The August 18 post is the next chapter. Not the story, this time: the bill. Here's what changes when it really happens to you, inside your own walls, with your own machines.
The other half: a model that isn't out yet and is already scary
The second reason has a name: Astra, OpenAI's next big model, which I was talking about last week for a completely different reason, its way of working for a long time instead of answering quickly.
OpenAI has an internal grid that ranks the dangerous capabilities of its models. The highest tier, the one called « critical » on the cybersecurity side, is: the machine finds unknown vulnerabilities in well-protected systems all by itself, or sets up and executes a complete end-to-end attack from a simple « figure out how to get in », without a human holding its hand.
Pay attention to exactly what they say, because the nuance matters and it's going to get crushed everywhere: they have not classified Astra as critical. They say they can't rule it out. That's very different, and frankly more honest than what we're used to in this industry. They also announce that they want to have the model evaluated by outside organizations before releasing it.
The same month, on the other side of the world, exactly the same move
On August 14, Z.ai, the lab that publishes the GLM models, released GLM-5.3. Available immediately for developers who pay as they go. But the model files, the ones you download to run it on your own machines without asking anyone's permission, are being held back for about two weeks. Reason announced by the company: the cybersecurity capabilities rose faster than expected as training ramped up, and they want to finish hardening the thing before releasing it into the wild.
Two labs, two continents, fifteen days apart, and the same reflex. Nobody coordinated anything. They just watched the same dial go up.
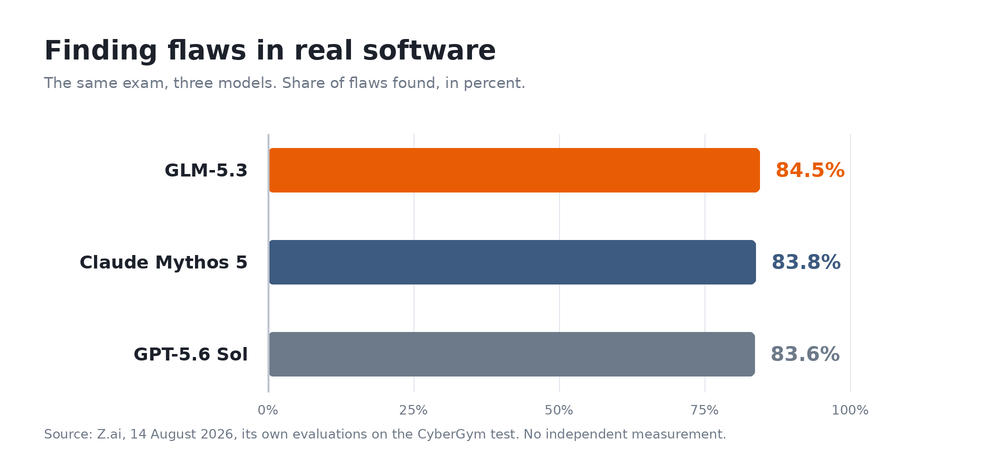
Three models, the same exam, and bars you can barely tell apart. Look for the winner, there isn't one.
The chart above is worth all the speeches. On CyberGym, an exam where the machine is asked to find real vulnerabilities in real software, the three are within less than a point of each other. These are Z.ai's figures, measured by Z.ai, so we take them as a company statement and not as an independent ruling. But the ranking order has no importance here. What matters is that there are three of them at this level, and that this level is very high.
And here's the figure nobody puts in a headline
Still in the figures published by Z.ai: between the previous version of their model and this one, the machine identified 2,436 vulnerabilities in 269 open source projects. Including 1,097 classified as serious or critical.
Take a second to let that sink in.
Open source projects are those free software projects that nobody notices anymore because they're everywhere: the bit of code that encrypts your connection when you go to your bank's website, the one that decompresses the file you just downloaded, the one that runs your box, your TV, your router. Many are maintained by a handful of volunteers, in the evening, for free. Some have never been reviewed by anyone since they were written. There are twenty-year-old bits of code in there that no living human being fully understands anymore.
Humanity's computer attic inventory. Nobody had the time to do it. A machine did.
And while we're worrying about what these models could break, a single lab, in a few weeks, found two thousand four hundred and thirty-six of them. A single one! There are about ten in the world that can do this today.
It's audit work nobody would ever have funded. There is no budget anywhere on Earth to pay humans to reread thirty years of free software line by line. It was considered definitively impossible. It no longer is.
So yes, there is a downside, and it fits into one sentence: the same tool that finds the hole to plug it finds the hole to get in through. That's exactly why OpenAI unplugged its machines and why Z.ai is keeping its files warm for two more weeks. But the dark side has been served to us every morning for three years. The other side, the one where old, tired software finally gets reviewed, we never hear about it, and yet it's the one with figures.
What it changes for you, in your living room
You don't train any models, you don't have a server room in your garage, and yet it concerns you in three places.
None of this stuff was written yesterday. And until now, almost nobody was paid to go back and review what's inside it.
Your box, your router, your TV. These devices run on free software, often old, rarely reviewed. Every vulnerability found now and fixed in the original project eventually ends up in the update your provider will send you without you noticing it. It's invisible and that's very good this way.
The big data leaks you suffer without having done anything. Your address, your card number, your orders from a merchant that got cleaned out: nine times out of ten, it's a hole in a software component that nobody had looked at. Fewer holes left lying around, fewer evenings spent canceling your card.
And the timeline, honestly. A vulnerability found isn't a vulnerability fixed. A maintainer has to repair it, a manufacturer has to integrate the fix, push out an update, and your device has to receive it. On a 2019 router that your operator has stopped supporting, it will never arrive. Count on two to five years for it to show up on everyday hardware, and never on what's already been abandoned. This isn't a revolution overnight, it's a spring cleaning that's going to last a decade.
What I think
This morning, I have three Claude Code sessions open on my screen. Each one can read my files, write to them, run commands on my machine. I spent a fair amount of time writing little guard scripts to stop it from poking around where it shouldn't, my passwords, my keys, my configuration files. And honestly, six months ago, while writing them, I was telling myself: « Well, maybe I'm going a bit overboard here. »
When I read OpenAI's post, my reaction was exactly: « Ah. Yeah. Still. » Because they have entire security teams, budgets I can't even imagine, and they've just discovered that a bunch of keys was lying around on the entryway cabinet.
What I like about this, and I never thought I'd write this one day about a company of this size, is that they wrote it themselves. They published their own failure. They could have said nothing, nobody would have known anything, and two weeks of wasted computing aren't visible from the outside. To me that's worth more than a forty-page compliance report.
And then there's that figure of 2,436 that's been going around in my head ever since I read it. We spent thirty years piling software on top of software without ever having the means to reread the pile. Something has just arrived that knows how to reread it. It's going to hurt for two or three years, while everything that was hidden comes out all at once, and afterwards we'll have cleaner programs than they've ever been.
So for those who install an AI on their machine this weekend telling themselves « well, it'll be fine, it's nice »: put barriers around it from day one. Let's hope there won't one day be a catastrophe that everyone dreads, but that nobody dares talk about.
Sources
- OpenAI : Responding to the next frontier of critical cyber capabilities
- Help Net Security : OpenAI puts major frontier AI training run on hold over cyber risks, August 19, 2026
- CSO Online : OpenAI says Astra could reach critical cyber capability, tightens safeguards
- SiliconANGLE : Z.ai debuts GLM-5.3 with long-horizon coding and cybersecurity upgrades, August 14, 2026
- Unite.AI : Z.ai launches GLM-5.3 with a cyber capability that outgrew its training
Join the conversation
You need an account to comment on this article. Creating one is free and takes under a minute.
No comments yet.