Apple warned users in 110 countries. No, spyware doesn't get in through a downloaded game.
On Thursday, Apple sent a new wave of threat notifications to users in 110 countries. It's the biggest one since the program launched in 2021. It now covers more than 150 countries. The alert appears in red on the lock screen, in Settings and on the account page. Apple also sends an email.
The door is armored, with twelve locks. The problem is the mail slot.
And then everyone asks the same question. I was asked it again yesterday : where does it get in? A downloaded game? A booby-trapped app? Which one needs to be deleted?
Short answer : none. And that's exactly what bothers people.
Nobody installed anything
These spyware programs are called mercenary because they are rented out to governments. They don't come through the App Store. No game, no flashlight app, no attachment to open. They can get in through a message you haven't even read.
The mechanism is simple. When your phone receives a photo, a video or a call, it doesn't just display it. It analyzes the data to prepare a preview, recognize the format and check that the file really matches what it claims to be. All of this happens automatically, before the slightest bubble even appears on the screen. If the code responsible for analyzing the file contains an error, a file designed to trigger that error may be enough. The attack is then launched. Without you.
The package explodes at the sorting center. You're in the living room, your mailbox is empty and you didn't ask for anything.
This isn't a theory. Citizen Lab, a University of Toronto laboratory known for its work on the subject, documented the case of two journalists. Their iPhones were infected by Graphite, the software made by the company Paragon. The entry point was a flaw in the processing of a photo or video shared through an iCloud link. This flaw, referenced as CVE-2025-43200, was exploited through iMessage accounts. No click was necessary. Apple fixed it in iOS 18.3.1.
Here we go again last February with CVE-2026-20700. This flaw caused memory corruption, meaning an error in the way a system component uses data in memory. Google's Threat Analysis Group discovered it. In its own bulletin, Apple describes it as "exploited in an extremely sophisticated attack against specifically targeted individuals". It was combined with two other flaws fixed in December. Three holes lined up for a single burglary.
Why it won't happen to you, and the price proves it
You're going to tell me : if my phone can be compromised without me doing anything, I'm screwed. No. The strongest argument isn't even technical. It's financial.
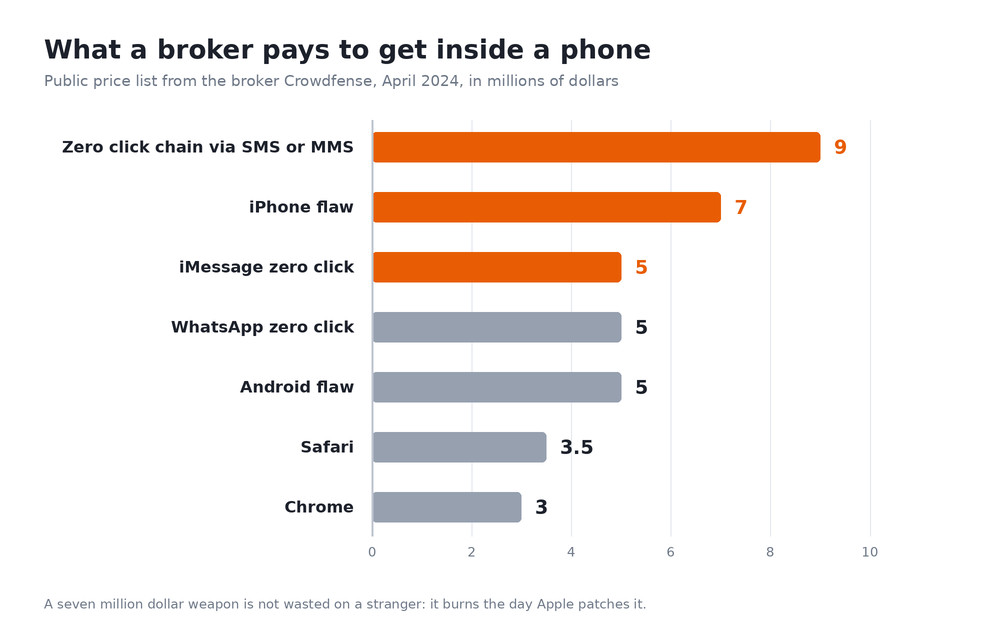
Seven million for a gateway. That puts a damper on the urge to use it on Joe Public.
These figures come from the public pricing list of a vulnerability broker, published in April 2024. A complete attack chain, meaning several vulnerabilities combined to take control of an iPhone by SMS and without any interaction, can sell for up to nine million dollars. This weapon is disposable too. As soon as Apple fixes the vulnerabilities, it is worth nothing. Nobody burns a seven-million-dollar round to read the messages of some guy who orders pizzas.
That is why Apple keeps repeating that these attacks are extremely rare and target specific people: journalists, lawyers, opponents, diplomats or executives. If you don't fit into any of these categories, your main risk probably isn't there. It's elsewhere. And it's much dumber.
Where it really gets in, at your place
Here, on the other hand, we do find apps and clicks. There are three main doors, in order of frequency.
On the right, the realistic version. No hooded hacker, just someone who knows your code.
The first is the configuration profile. It's a settings file that you install yourself. Originally intended for businesses and schools, it can redirect your traffic or add a certificate that makes it possible to control certain connections. A fake support call, a link, two buttons, and the profile is installed. Nobody hacked anything. You were simply convinced to do it yourself.
The second is two minutes alone with your unlocked phone. Stalkerware is often installed like that. No need for a seven-million-dollar vulnerability when someone knows their partner's code.
The third is your Apple ID. Here, there is no software to install. With your password, someone can access the iCloud backup, and therefore the messages and photos, from anywhere. It's the most discreet door of the three. And the one we always forget.
Ten minutes tonight, in the settings
Okay, let's get practical. Here are four places to check, in order. This goes for the whole family.
Réglages > Général > VPN et gestion de l'appareil
Réglages > [ton nom] > liste des appareils, tout en bas
Réglages > Temps d'écran
Réglages > Confidentialité et sécurité > Vérification de sécurité
In the first menu, there shouldn't be any profile that you didn't install yourself. If this phone has never been configured by a school or a large company, the list should be empty. In the second, check that you recognize every device connected to your account. If not, disconnect it. The third can hide restrictions installed by someone else. The fourth is designed for situations where you don't feel free to quietly look around. It lets you cut off all current sharing at once.
And, obviously, install the updates. This isn't advice from some old fossil. The vulnerabilities mentioned above remain dangerous as long as they haven't been fixed on your device. The time between the publication of the fix and its installation, that's exactly the window of opportunity.
Lockdown Mode, and what it costs you
Lockdown Mode is the option Apple recommends to people who receive this notification. It has existed since iOS 16 and its results are frankly good. In March, Apple said it was not aware of any successful attack of this kind against a device protected by this mode. Citizen Lab has also documented at least two cases where it blocked an attack in progress.
This mode isn't magic. It reduces the attack surface by cutting off functions, so you pay for it in comfort. It blocks most attachments in messages, except images. It disables complex web technologies, which can break certain sites. It refuses 2G and 3G, Wi-Fi networks considered dubious, wired connections with another device and calls from unknown numbers. It also prohibits the installation of a configuration profile.
In other words, it closes the mail slot. If you're a journalist, lawyer or executive, activate it and live with its constraints. If you're a plumber in Grez-Doiceau, you'll mostly risk getting annoyed with your phone.
If you really receive the notification
One detail worth knowing, because this alert has become the best scam pretext around. A genuine Apple notification never asks you to click on a link, open a file, install an application or a profile. It does not ask for your password or a verification code either, whether by email or by phone. Never.
There is only one good way to check the alert. Open account.apple.com yourself, then log in. The notification should appear at the top of the page. If it is not there, it is fake. If it is there, Apple advises calling the emergency line of the NGO Access Now, which offers this help for free.
What I think
There is good news hidden in this story, and nobody really puts it that way. Taking control of an iPhone remotely requires several previously unknown flaws combined and costs several million dollars. It shows that the security of the gizmo holds up damn well. We complain about Apple and its closed garden, but that is also what makes this door so expensive to open.
The bad news is that an entire market makes a living from reselling these keys. The prices are displayed like in a spare parts catalogue. And, for most targets, the only warning comes from a notification sent by the phone manufacturer. As a safety net, we have seen more reassuring.
So no, your nephew will not install Pegasus on you with a crappy racing game. But tonight, take a look anyway at the list of profiles and devices connected to your account. It takes two minutes. And that is where the real nasty surprises are hiding.
Join the conversation
You need an account to comment on this article. Creating one is free and takes under a minute.
No comments yet.